
Your team and their roles
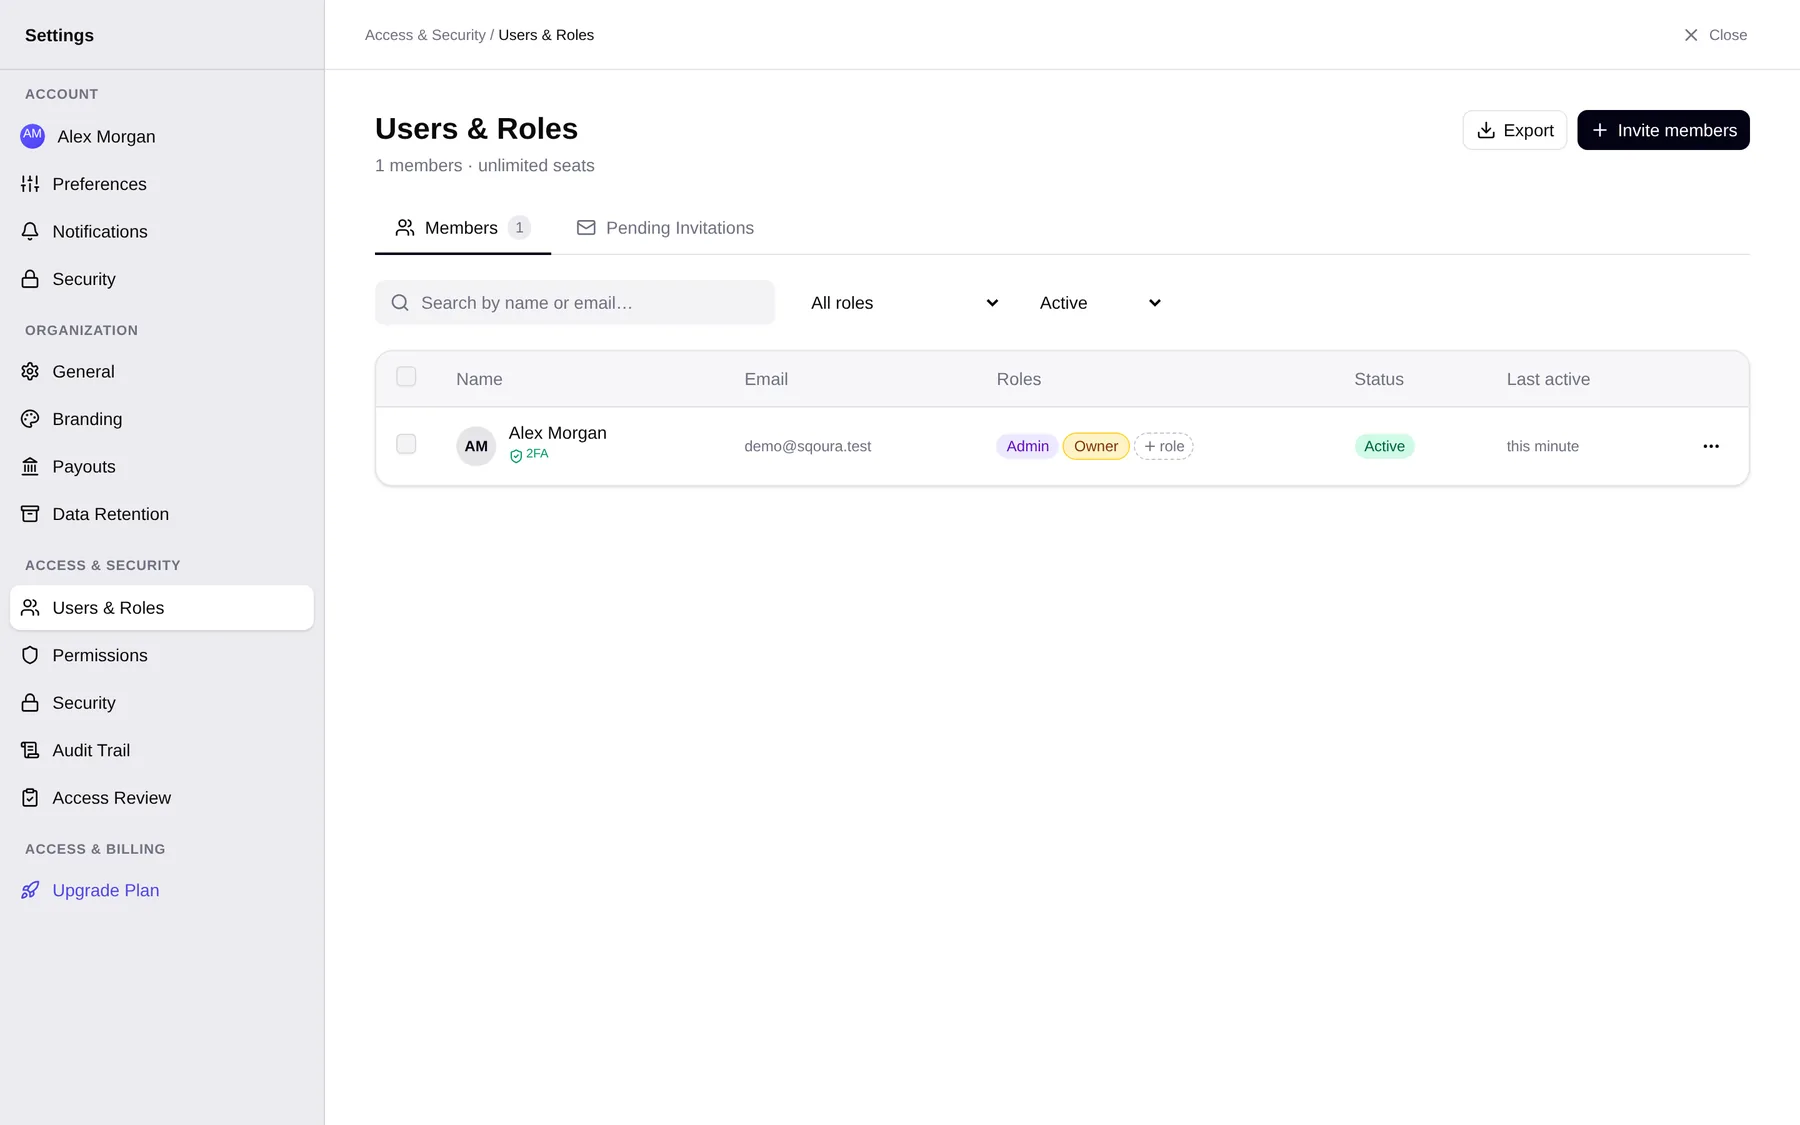
Your team lives under Access & Security → Users & Roles. Opening it needs the View org members permission, which every built-in role except Competition official holds. Someone without it is told “Your role does not include access to team members.” Changing anything on it needs Manage custom roles — with the built-in roles, Owner and Admin — and without that a banner reads “You have read-only access. Contact an Admin to manage users and roles.”
Under the heading you get either “N of M seats used” or “N members · unlimited seats”, then two tabs — Members and Pending Invitations — each with a count. The list refreshes itself every 30 seconds and whenever you come back to the tab.
Export downloads your member list as a spreadsheet file with each person’s name, email, roles, status, whether they have two-factor authentication enrolled, when they were last active and when they joined.
Inviting colleagues
Section titled “Inviting colleagues”- Press Invite members.
- Type addresses into Email Address(es), pressing Enter or a comma after each. Each one becomes a removable pill, so you can invite several people at once.
- Choose a Role. Every built-in role except Owner has a card saying what it is for, and any custom roles you have built appear below them. Nobody can be invited as Owner — ownership is handed over, not granted.
- Add a personal message if you want one.
- Send. You get Invitation sent to <email> or N invitations sent, and the view switches to Pending Invitations.
If you add more addresses than you have seats, a Not enough seats warning appears before anything is sent, with an Upgrade Plan → link. If the server refuses the send, the message is Seat limit reached. Inviting someone who is already a member is not an error — you are simply told.
Pending invitations
Section titled “Pending invitations”The table shows Email, Role, Invited by, Sent and Expires, and each row has Resend and Cancel.
| What happens | Detail |
|---|---|
| Expiry | 7 days. In the last 24 hours the column turns amber and counts down in hours; after that it reads Expired. |
| Resend limit | Each invitation can be resent a fixed number of times — “Resend limit reached (N max). Cancel and re-invite if needed.” |
| Resend cooldown | You must wait between resends — “Please wait N minutes before resending again.” |
| Cancel | Removes the invitation immediately and frees the seat. |
An expired invitation cannot be revived. Cancel it and invite the person again.
What your colleague sees
Section titled “What your colleague sees”They follow the link in their email, and the page asks for whatever it needs:
- They already have a Sqoura account — they enter their existing password.
- They do not — they set a full name and a password of at least 12 characters, with a strength meter beside it.
The screen then reads You’re in and names your organisation, and they are signed in straight away. There is no separate login step.
An expired or already-used link shows Invitation expired; a broken one shows Invalid invitation. In both cases the only way forward is a fresh invitation from you.
The built-in roles
Section titled “The built-in roles”Roles are additive. One person can hold several, and what they can do is everything their roles allow put together. Granting a role never removes one.
| Role | What it is for |
|---|---|
| Owner | Everything an admin can do, plus billing, where payouts go, and transferring ownership. |
| Admin | Runs the organisation: every tournament, entry and payment, members and roles. |
| Tournament director | Runs competitions end to end: setup, draws, closing, results, qualification and season rules. |
| Registrar | Reviews and approves entries, builds registration forms, and sends athletes their links. |
| Finance | Payments, waivers, refunds, exports and earnings. |
| Competition official | Competition day: weigh-in readings, check-in and entering scores. |
| Staff | Day-to-day operations: set up tournaments, review entries, make draws, take payments. |
| Viewer / auditor | Read-only access to everything, including the activity log and the access review. |
Those descriptions are the ones the product shows on the invite cards and on Access & Security → Permissions, where you can open each role and see every permission it holds.
Owner and Admin
Section titled “Owner and Admin”Whoever creates the organisation holds both. There is exactly one Owner. The owner cannot be deactivated or removed, and is the only person who can change where payouts are sent or hand the organisation to somebody else.
Admin holds everything else — every permission except Change payout account and Transfer ownership. Several people can be admins, and an organisation always keeps at least one.
What the other roles can do
Section titled “What the other roles can do”| Area | Tournament director | Registrar | Finance | Competition official | Staff | Viewer / auditor |
|---|---|---|---|---|---|---|
| Tournaments | Everything except delete and manage IWUF/organisation defaults | View | View | View, take weigh-in readings, check athletes in | View, create, edit, publish and start, generate and publish draws, schedule sessions, take weigh-in readings, check athletes in | View |
| Results | Record, finalise and correct finalised | — | — | Record | Record | — |
| Qualification | Everything | View | — | — | View, promote into qualifying places, change team rosters | View |
| Seasons | View, plan, change season rules | View | View | — | View, plan | View |
| Athletes | View, manage and send links, replace every link, resolve identity reviews | View, send links, resolve identity reviews | View | View | View, send links, resolve identity reviews | View |
| Entries | View, export, read internal notes | View, approve, reject (also in bulk), walk-in registrations, edit, read and add internal notes, check original documents | View, export, read internal notes | View | Same as Registrar | View, read internal notes |
| Forms | View, close, reopen | View, create, edit, publish, close, reopen, manage templates | View | — | Same as Registrar | View |
| Payments | View | View, review slips, record offline payments, resend invoices | View, review slips, record offline payments, resend invoices, refund through the payment provider, waive, approve waivers, export | — | Same as Registrar | View |
| Earnings and payouts | — | — | View earnings, view payout account | — | — | — |
| Scanning | Pair a scanning phone | Pair a scanning phone | — | Pair a scanning phone | Pair a scanning phone | — |
| Organisation | View members and settings | View members and settings | View members and settings | View settings | View members and settings | View members and settings, review access |
Only Owner and Admin can delete a tournament, delete a form, merge two athletes, delete somebody else’s internal note, see identity numbers, waive original documents, invite or manage members, or build custom roles.
Separations worth knowing
Section titled “Separations worth knowing”Some things that look like one job are deliberately two permissions, and these are the ones people ask about:
- Recording a refund you handed over yourself is separate from issuing a refund through the payment provider. Only Owner, Admin and Finance have the second.
- Recording a result, finalising it and correcting a finalised result are three different permissions. Officials and Staff only record.
- Changing a qualifying place is separate from publishing qualification, because publishing is what tells the athletes.
- Generating a draw is separate from running a weigh-in, matching the split between the chief registrar and the scheduling group.
- Checking athletes in is separate from editing the tournament, so the desk you staff on the morning cannot rewrite your category structure.
- Seeing identity numbers is Owner and Admin only, precisely because other roles can view and export entries.
- Waiving a fee and approving a waiver are separate, so that a second person can be required to agree — see Requiring two-factor authentication for where that switch lives.
- Pairing a scanning phone is its own permission, separate from reading entries.
Custom roles
Section titled “Custom roles”- Press New Role in the left column of Access & Security → Permissions. Getting to that section needs Manage custom roles.
- Give it a Role name (up to 80 characters) and an optional Description (up to 255), then Create role.
- The role is created holding nothing. Tick what it should hold in the right-hand checklist — whole sections can be ticked at once.
- A footer appears reading “You have unsaved permission changes.” Press Save changes and you get Permissions saved.
Edit details changes the name and description. Delete removes the role, and if anyone holds it you are made to reassign them first — the dialog names how many people are affected and offers Reassign affected members to any built-in role except Owner, or another custom role.
The checklist is generated from what the server actually enforces, so it is always the truth about what a permission does. Dangerous permissions are flagged in it. Some imply others — granting Invite org members, Manage org members or Manage custom roles carries View org members with it, and Manage org settings carries View org settings.
How many custom roles you get depends on your plan: Free 1, Club 3, Federation 10, Enterprise unlimited. Your usage against that shows on the Usage card in Organisation settings.
Changing someone’s role
Section titled “Changing someone’s role”- On the member’s row press the dashed + role chip, or open the ⋯ menu and choose Grant role.
- The dialog explains “Add an additional role to <name>. Existing roles are not removed.”
- Pick a Role from the ones they do not already hold. Owner is never offered.
- Optionally set an Expiry, as a date plus an hour and minute. Leave it blank for permanent. An expiry in the past is refused, and a role due to expire within 24 hours carries a small clock on its badge.
- Optionally give a Reason. The label tells you it is written to the audit log, and it is worth writing.
- Press Grant role.
To take one role away from someone who holds several, hover its badge and press the small ×. You are asked to confirm — Revoke <role> role? — and offered a reason box that is also written to the audit log.
Two refusals you may meet: “Cannot revoke: this is the last admin in the org.” and “Cannot revoke: member must hold at least one role.” Both are enforced by the server — an organisation always keeps at least one active admin, and a member always keeps at least one role.
A role change takes effect on that person’s next request, not instantly in a tab they already have open.
Access to one tournament or season
Section titled “Access to one tournament or season”A volunteer who scores on competition day, or the director of this year’s championship, does not need that role across your whole organisation. Open the ⋯ menu on their row and choose Access to one tournament…:
- Pick the Tournament or season. A season covers every tournament in it.
- Pick the Role. Every built-in role except Owner and Admin can be given this way — those two are organisation-wide by nature.
- Choose when it Ends: When the tournament ends, On a date, or When removed.
- Optionally give a reason, kept on the record.
They get that role only inside what you chose; their access everywhere else stays as it is. The grant shows on their row as the role and the tournament’s name, and the small × beside it removes it early.
Transferring ownership
Section titled “Transferring ownership”Only the owner sees Transfer ownership… in the ⋯ menu. The new owner takes over billing, where payouts are sent, and who owns the organisation; you stay an admin. You type TRANSFER to confirm, because only the new owner can transfer it back.
Requiring two-factor authentication
Section titled “Requiring two-factor authentication”Under Access & Security → Security, the Security policy card has Require two-factor authentication for, with a box per built-in role. Members in a ticked role must set up an authenticator app before they can use the organisation, and cannot turn it off. Owner is always ticked; Admin, Tournament director and Finance are ticked by default. Changing it needs Manage org settings.
The same card holds A second person approves every waived fee. When it is on, waiving a fee files a request and the fee stays owed until someone else with Approve fee waivers agrees.
Deactivating and removing
Section titled “Deactivating and removing”The ⋯ menu on each row also offers:
| Action | What it does |
|---|---|
| Role history | Every grant and revocation for that person — who did it, when, the reason given and any expiry, 20 at a time. |
| View activity | What that member has been doing. |
| Deactivate | They lose access immediately and can be brought back later. Needs a second-factor code. Refused with “Cannot deactivate: last admin.” Not offered for the owner. |
| Reactivate | Restores a deactivated member. |
| Remove member | “This permanently removes them from the organisation. All role grants will be revoked. This action cannot be undone.” Not offered for the owner. |
Ticking the checkboxes reveals a bar reading N selected with Deactivate, Remove and Clear for doing the same to several people at once.
Finding people
Section titled “Finding people”Above the table are a search box (“Search by name or email…”), a role dropdown starting at All roles, and a status dropdown offering All statuses, Active and Inactive. Name, Email and Last active all sort, and pages hold 25 members.